In the meantime...to brighten your day, here is a music video co-authored by yours truly about the woes of compilers, gdb, and autograders for programming homework to the tune of Taylor Swift's "Shake It Off."
Monday, September 14, 2015
A Musical Interlude to Medical Device Security
We at Archimedes have been busy running security engineering tutorials at medical device manufacturers and hospitals over the past several months, so we have not had the opportunity to post new material lately. We are also in the middle of scheduling various seminars on medical device security at hospitals as part of October's National Cybersecurity Awareness month.
In the meantime...to brighten your day, here is a music video co-authored by yours truly about the woes of compilers, gdb, and autograders for programming homework to the tune of Taylor Swift's "Shake It Off."
In the meantime...to brighten your day, here is a music video co-authored by yours truly about the woes of compilers, gdb, and autograders for programming homework to the tune of Taylor Swift's "Shake It Off."


Saturday, July 25, 2015
When Will a Medical Device Endure a Cybersecurity Recall?
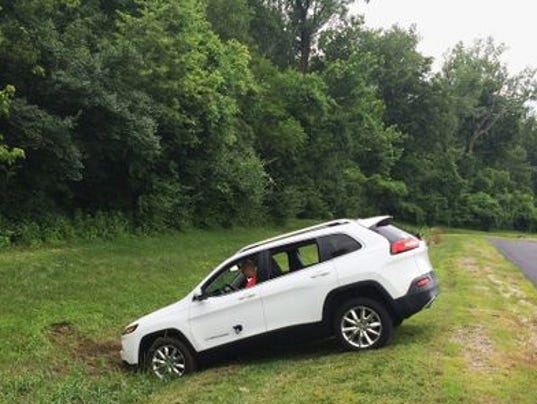 |
| Cybersecurity for the Internet of Things: A house of cars? |
Issuing a recall is no light matter because there are subtle risk-benefit implications. For instance, a sudden recall on a medical device could have profound risks that outweigh the benefits of a blanket recall. In a non-cybersecurity context, this debate arose not long ago when a defibrillator lead suffered a mechanical design flaw. Because removal of an electrode could pose risks to a patient when the tip had already bound to the cardiac tissue, only certain patients were recommended to replace the electrode. So whereas today automobiles have been recalled for cybersecurity reasons, there will need to be a different debate when eventually some medical device will suffer a clinically relevant cybersecurity flaw. If the flawed device is not implanted and other competing devices are available, then a recall may make sense in the risk-benefit calculus as patients can use another device (e.g., an infusion pump or bedside monitor). On the other hand, blanket recalls are likely not the answer for an implanted device where there are fewer alternatives available for patients already with certain predisposed risks.
The medical device community should consider itself lucky that the automotive community has earned the dubious honor of having the first cybersecurity-only recall. Given the large number of medical devices, it's just a matter of time before some medical device company will receive a painful, late night phone call to confront challenges similar to what Fiat Chrysler is now enduring.
Monday, March 23, 2015
How I Met Your Founder: Kevin Fu Meets Earl Bakken of Medtronic
 |
| Earl Bakken and Kevin Fu discussing blended medicine, January 2015 |
I have to admit, nine years ago I would not have predicted that I'd be having a private lunch conversation about blended medicine with Earl in his home. Back in 2006, I became intensively preoccupied with understanding and improving the security and privacy of implantable medical devices. It took a couple years, but after a rejection, one of our first papers on medical device security was eventually published at the IEEE Symposium on Security and Privacy in 2008. Needless to say, there was initially some mutual mistrust between various parties. Here's this academic from the ivory tower warning of security problems from the future! It's only natural to be suspicious.
Fast forward to 2015, and you'll find that many major medical device manufacturers understand the importance of cybersecurity, but are still working on their solutions under the spirit of NIST and AAMI security and risk frameworks. There are growing pains. That's why each May, top engineers from the medical device industry and healthcare providers descend on Ann Arbor for interdisciplinary group problem solving at the Archimedes Workshop on Medical Device Security.
I've got quite the tome of notes from my discussion with Earl, so I'll be updating this blog entry with stories as I get a break from teaching a large undergraduate class this semester. Stay tuned for the next photo and story!
Fast forward to 2015, and you'll find that many major medical device manufacturers understand the importance of cybersecurity, but are still working on their solutions under the spirit of NIST and AAMI security and risk frameworks. There are growing pains. That's why each May, top engineers from the medical device industry and healthcare providers descend on Ann Arbor for interdisciplinary group problem solving at the Archimedes Workshop on Medical Device Security.
I've got quite the tome of notes from my discussion with Earl, so I'll be updating this blog entry with stories as I get a break from teaching a large undergraduate class this semester. Stay tuned for the next photo and story!
North Hawaii Community Hospital
 |
The radiologists hang loose at North Hawaii Community Hospital, and have a funny sense of humor. |
Subscribe to:
Posts (Atom)