Tuesday, January 19, 2016

Postmarket Management of Cybersecurity in Medical Devices: FDA Releases #2 Draft Guidance Document

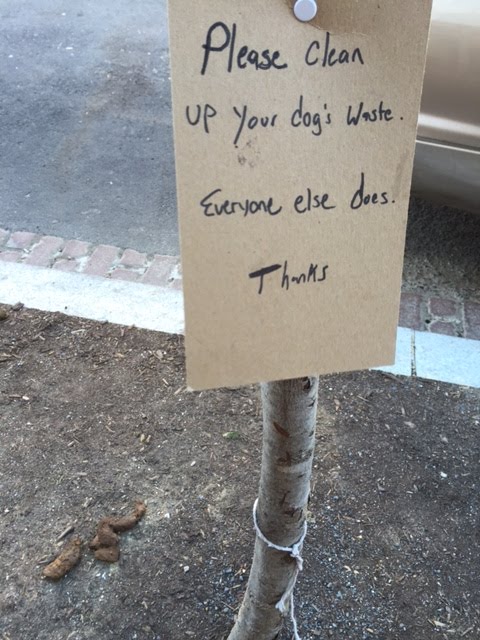
In the end, poost-market medical device
security is about peeople and respoonsibility. Photo
taken today outside the Washington Convention
Center meeting on automotive cybersecurity.
FDA has unleashed its long-awaited #2 guidance document on cybersecurity: its draft post-market guidance on medical device security. Ok, ok, I conclude my Secure Health IT humor here.

I'd like to commend FDA for releasing this difficult to write document. To the arm chair engineer, one might think this is easy stuff. Wrong. While the already finalized pre-market guidance primarily focuses on basic engineering practices to build security into medical device designs, the post-market guidance is mostly about people and effective communication. Why is writing post-market guidance so difficult? Because it's more about people than technology.

There's a lot that the FDA guidance gets right, and most of my criticism pertains to word choice (and lack of puns) that can be solved by editing. The preamble of the document (that focuses on networked medical devices) does not entirely match the body of the document (that talks about all devices, not just networked). The terms "networked devices” and “connected" are red herrings. A network is not necessary for an cybersecurity exploit; malware gets in just fine by unhygienic USB drives carried by unsuspecting personnel. Social engineers still use telephones to trick personnel into enabling unauthorized remote access. The final post-market guidance will need to more deliberately draw attention to outcomes of compromise and risks of vulnerabilities rather than the constantly evolving modality of delivery of exploits. After all, when we talk about surveilling for the spread of flu, we don't limit discussions to spread by cough versus spread by sneeze. Should the document list networked and connected devices as examples of infection vectors? Yes. Should it mention only networked and connected devices? No. Outcomes, not modalities.

What's my opinion on important post-market activities in general? Stakeholders need to communicate vulnerabilities more effectively, and monitor for shifting threats. Medical device manufacturers should create workflows to receive outside input on potential vulnerabilities.

Security folks who discover potential problems need be aware of timescales for responses to responsible security vulnerability disclosures. As Allan Friedman explains, even if you think you're the most important person on the planet, don't expect a medical device manufacturer to simply drop everything they are doing to fix a security flaw overnight. On the other hand, it boggles the mind why a manufacturer might wait a year to meaningfully respond to a clinically significant vulnerability reported by a security researcher.

I expect to see more FDA actions on the less noble manufacturers who do not catch up with this basic medical device security post-market guidance.

Thursday, December 3, 2015

FDA Hosts Workshop on Medical Device Cybersecurity in 2016


I'm pleased to announce that FDA will be holding its 2nd workshop on Collaborative Approaches to Medical Device Cybersecurity on January 20-21, 2016 at FDA's White Oak headquarters. This public workshop will bring together the stakeholders who have been communicating over the last couple years to find collaborative ways to improve rather than whine about medical device security.

On everyone's minds is the anticipated FDA guidance document on post-market cybersecurity as well as the AAMI guidance document on medical device security that many of us have been toiling over for multiple years to help medical device engineers incorporate cybersecurity best practices into the early requirements engineering, design, and implementation of medical devices.

For others in the cyberphysical systems space, one might come a day early because the National Highway Traffic Safety Agency will be holding a suspiciously similarly sounding Vehicle Cybersecurity Roundtable on January 19, 2016!

All these interesting workshops will be leading up to the 4th Annual Archimedes Workshop on Medical Device Security in May 16-17, 2016 in Ann Arbor, MI.

See you there!

Tuesday, September 29, 2015

Medical Device Security Report at the National Academy of Engineering FOE

Prof. Fu speaking with fellow engineers at the NAE Beckman Center.
Here you can find my newly released report "On The Technical Debt of Medical Device Security" from the National Academy of Engineering web site.

Earlier this month, I spoke about medical device security at the annual "Frontiers of Engineering" event held by the National Academy of Engineering. All the talks were captivating and intellectually stimulating, including topics such as the James Webb Space Telescope, nanostructured metamaterials, and forecasting natural disasters.

One of the more memorable talks was by Jeremy Banik of the Air Force Research Laboratory who demonstrated a high strain composite mechanism by unrolling an innocent looking 1 ft long Carbon Storable Tubular Extendible Member into a sturdy 20+ ft pole. The pole automatically unfurls and makes a rather loud snap as it zips itself up. It's designed for deployment in space where payloads that fit the geometry of a rocket must expand to carry out large-diameter space missions. The audience asked if TSA had ever tried opening the roll, and the answer is no, but it would be tubular, dude.
Carbon Storable Tubular Extendible Member. Photo from Jeremy Banik.